
PacketTiger 1SC Network Packet Broker
4x 10M/100M/1G/2.5G RJ45 Ports +2x 1G SFP+ Ports + 1x 1G RJ45/SFP Ports
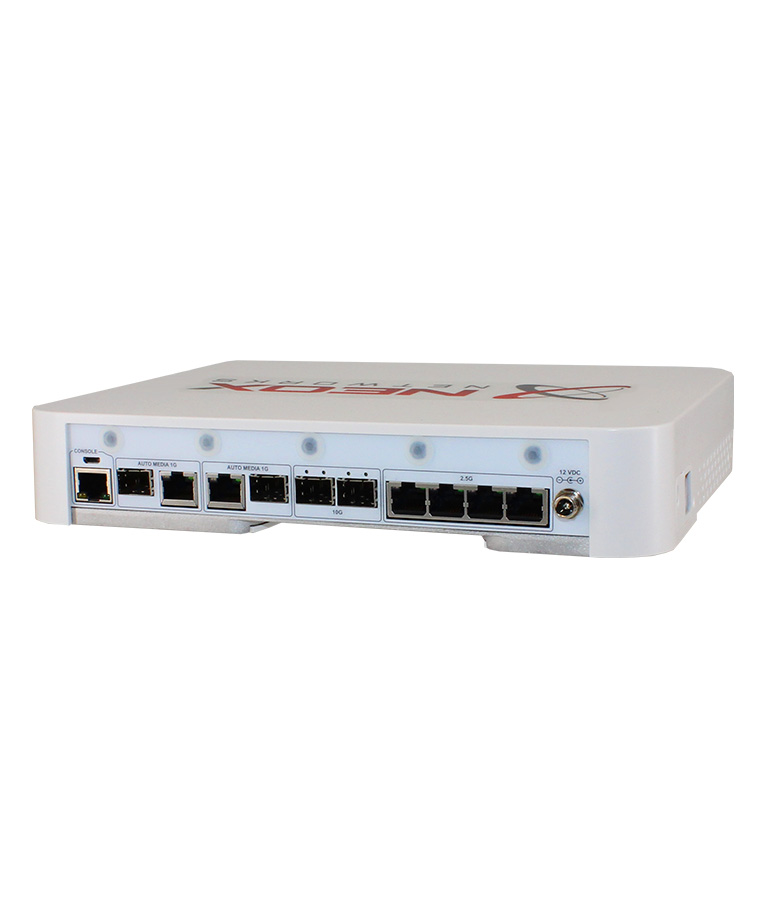


The PacketTiger 1SC is a next-generation Network Packet Broker designed for data centre and perimeter network environments, delivering efficient traffic management, optimised port utilisation, and enhanced network visibility. It can be deployed as a standalone L2–L4 filtering appliance or integrated into existing infrastructures to improve monitoring and security workflows.
Built with advanced packet processing capabilities, PacketTiger 1SC enables intelligent traffic handling through filtering, deduplication, masking, slicing, tunnelling, packet capture, and replay. Optional NetFlow/IPFIX and Deep Packet Inspection (DPI) provide deeper analytical insight into network and application traffic. The platform ensures scalable, high-performance packet handling with flexible deployment and hardware-accelerated processing.
- Optimises network visibility and monitoring efficiency in data centre and edge environments
- Supports standalone deployment or integration into existing packet broker architectures
- Advanced GTP correlation using F-TEID, IMSI, IMEI, APN, and inner IP parameters
- Data masking to protect sensitive packet-level information
- Packet deduplication removes duplicate traffic from monitoring pipelines
- Deep packet filtering across headers and payload with granular rule definitions
- Tunnel-aware processing for GTP, MPLS, GRE, L2TP, VXLAN, and related protocols
- Optional NetFlow/IPFIX generation for flow-based analytics
- Optional Deep Packet Inspection (DPI) for application-layer visibility
- Packet capture and PCAP replay for analysis and validation
- Nanosecond-accurate hardware timestamping for precise traffic monitoring
- Hardware acceleration via DPDK for high-performance processing
- Flexible port allocation: 1:1, 1:N, N:1, N:N traffic models
- Supports up to 1,000,000 filtering rules with AND/OR logic
- Advanced filtering for MAC, VLAN, IPv4/IPv6, TCP/UDP, DSCP, TCP flags, MPLS, GTP, L2TP, VXLAN, and regex-based rules
- User Defined Filtering (UDF) for custom packet matching
- Traffic aggregation and regeneration across interfaces
- Header stripping support for MPLS, PPPoE, VN-Tag, VXLAN, GRE, L2TP, GTP-U, and GENEVE
- Load balancing using 3-tuple, 4-tuple, and 5-tuple hashing
- Port labelling for traffic identification after aggregation
- Static and dynamic packet slicing for bandwidth optimisation
- Packet capture with ring-buffer storage support
- Packet replay for troubleshooting and validation testing
- Multiple management interfaces: CLI, SSH, SNMP v2/v3, Web UI, NetCONF, REST API
- AAA authentication via RADIUS and TACACS+
- Metadata export via Kafka integration
- Syslog and SNMP trap logging support
- GRE Layer 2 and Layer 3 tunnelling support
- VLAN editing and MAC address replacement
- High flexibility via NMC and multi-transceiver support
- Scalable architecture with clustering and HA support (future-ready)
- Digital Diagnostics Monitoring (DDM) support (upcoming feature)
- Simple deployment with easy configuration
- 4 × 10/100/1000M RJ45 Ports (supports up to 2.5G)
- 2 × 1G SFP+ Ports
- 1 × 1G RJ45/SFP Combo Port
- Port speeds supported: 10/100/1000M, 1G, 2.5G
- Connector types: RJ45, SFP, SFP+
- Product type: Hardware Appliance
- Product group: Network Packet Broker
- Vendor: NEOX NETWORKS
Datasheet – Download
Advanced Test, Measurement & Network Assurance Solutions